
blockchainIDsystem/README.md
README.mdRaw
1# blockchainIDsystem
2A blockchain based anonymous distributed login system
3
4### Warning! Academical version
5This version is only for academical purposes, is not a version to run in production. Everything has been developed from scratch (the p2p network, the blockchain, the RSA library, ...) to learn it deeply.
6Also this version is not finished.
7
8A new version of this project, being developed using libaries and Ethereum network, is in https://github.com/arnaucode/darkID
9
10### Main concept
11The objective is to guarantee a decentralized login system, but making sure that registered users are real ones and there are no bots generating large amounts of accounts. Only the verified (by email or phone) users can generate an anonymous ID (the Public-Key blind signed).
12
13
14
15
16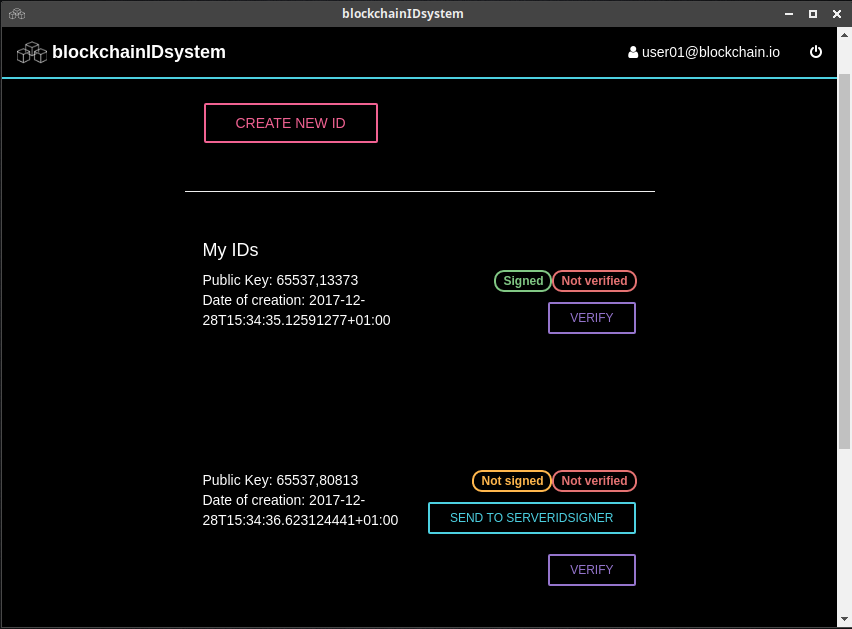
17
18## How it works?
19
20
21#### Network infrastructure
22
23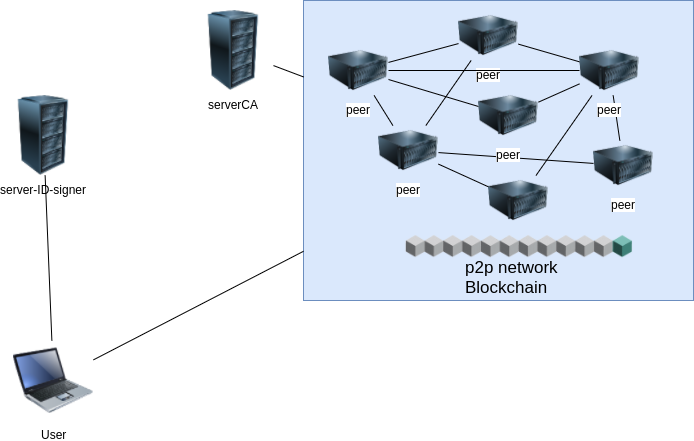
24
25There are different types of nodes:
26- peers
27 - the peers of the p2p network that runs the blockchain
28- serverCA
29 - Is a REST server that has been certified (is the Certified Authority) to validate the peers that will be able to participate of the blockchain.
30 - Have the webapp (frontend) to validate peers through a GUI interface
31 - The GUI frontend webapp allows also to view the current peers of the network and the blocks of the blockchain
32- server-ID-signer
33 - The server where the user creates a non anonymous account
34 - Also is the server that blind signs the Anonymous ID of the users
35 - Have the webapp (frontend) to interact through a GUI interface
36
37#### Step by step process
381. Once all the nodes of the network are running, a new user can connect to the server-ID-signer.
392. The user registers a non anonymous user (using email, phone, password, etc), and performs the login with that user
403. The user, locally, generates a RSA key pair (private key & public key)
414. The user blinds his Public-Key with the server-ID-signer Public-Key
425. The user's Public-Key blinded, is sent to the server-ID-signer
436. The server-ID-signer Blind Signs the Public-Key blinded from the user, and returns it to the user
447. The user unblinds the Public-Key signed by the server-ID-signer, and now has the Public-Key Blind Signed by the server-ID-signer
458. The user sends the Public-Key blind signed to the p2p network
469. The peers verify that the Public-Key Blind Signed is correctly signed by the server-ID-signer, if it is, they add the Public-Key to the Blockchain, inside a new block
4710. Then, when the user wants to login into a platform, just needs to put his Public-Key
4811. The platform goes to the Blockchain, to check if this Public-Key is registered in the blockchain
4912. The platform sends a message encrypted with the user Public-Key, and the user returns the message decrypted with the Private-Key, to verify that is the owner of that Public-Key
50
51
52##### RSA encryption system
53https://en.wikipedia.org/wiki/RSA_cryptosystem
54- Public parameters: (e, n)
55- Private parameters: (d, p, q, phi, sigma)
56- Public-Key = (e, n)
57- Private-Key = (d, n)
58- Encryption:
59
60- Decryption:
61
62
63
64##### Blind signature process
65https://en.wikipedia.org/wiki/Blind_signature
66- m is the message (in our case, is the Public-Key of the user to be blinded)
67
68
69- server-ID-signer blind signs m'
70
71
72- user can unblind m, to get m signed
73
74
75- This works because RSA keys satisfy this equation
76 and this 