
darkID-prototype/README.md
README.mdRaw
1# darkID: A proof of concept of an anonymous decentralized identification system based on blockchain
2Blockchain based anonymous decentralized ID system
3
4( Full slides in: https://github.com/arnaucode/darkID/blob/master/darkID-presentation.pdf )
5
6## 1.- Main concept
7The main idea behind darkID is to implement a proof of concept of a decentralized system that allows platforms to identify verified users, but ensuring their anonymity.
8The main point, is to ensure anonymity, but at the same time, allow users to verify their identity, to ensure that no fake accounts are being used.
9
10
11## 2.- How it works
12
13- Verify the non anonymous ID of an user
14 - Based on the: username, email, phone, ID card, etc
15- From a logged and verified user, generate an anonymous darkID (Public Key, and save the Private Key into the storage), and get that darkID signed by an authority (serverIDsigner), with high reputation, and without knowing what is signing, to ensure the anonymity of the user
16- Once the darkID (Public Key) is signed by an authority server, add the darkID to the blockchain (ethereum, or some other)
17- Use the darkID to authenticate in platforms (just need to point the darkID reference in the blockchain), and the platform will send a challenge to the user, to resolve it with the Private Key assigned to the darkID from the darkID desktop app.
18
19```go
20type DarkID struct {
21 ID string `json:"id"`
22 PrivK string `json:"privK"` //path of the PrivK file
23 PubK string `json:"pubK"` //path of the PubK file
24 PublicKey string `json:"publicKey"`
25 Date time.Time `json:"date"`
26 Hashed []byte `json:"hashed"`
27 UnblindedSig []byte `json:"unblindedsig"`
28 Verified bool `json:"verified"`
29 ServerVerifier *rsa.PublicKey `json:"serververifier"`
30 SignerID string `json:"signerid"`
31 BlockchainRef string `json:"blockchainref"`
32}
33```
34
35### 2.1.- Infraestructure
36
37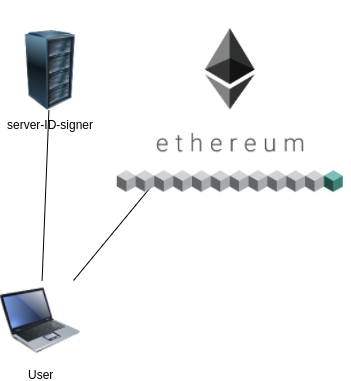
38
39
40#### 2.2.1.- serverIDsigner
41- The server where the user creates a non anonymous account
42- Also is the server that blind signs the anonymous ID of the users
43- This server must be a recognized authority, or based on some reputation system. As only the reliable serverIDsigner will be used by the users to trust their ID validation
44- The serverIDsigner, can be different servers, based on a public reputation, where the users trust the servers that their are using to verify their darkIDs.
45
46#### 2.2.2.- ethereum Smart Contract
47Where the darkID is stored. In this case, is a very simple smart contract.
48
49#### 2.2.3.- Desktop app
50An electron desktop app implemented in Angularjs and Go lang.
51
52
53
54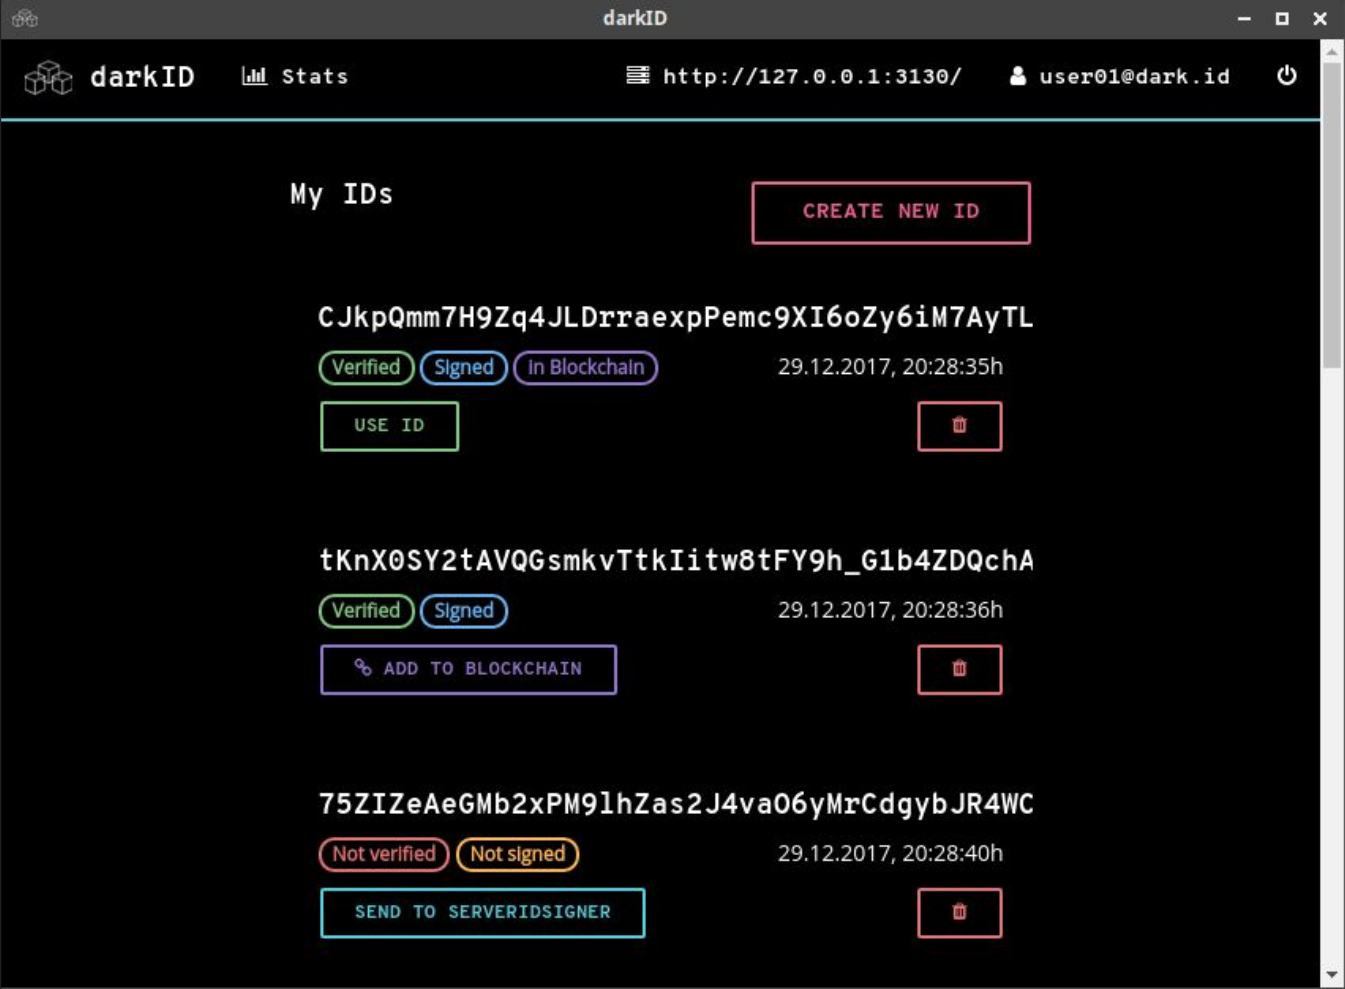
55
56
57
58
59### 2.2.- Step by step process
60
61- Once all the nodes of the network are running, a new user can connect to the serverIDsigner.
62- The user registers a non anonymous user (using email, phone, password, etc), and performs the login with that user
63- The user, locally, generates a RSA key pair (private key & public key)
64- The user blinds his Public-Key with the serverIDsigner Public-Key
65- The user's Public-Key blinded, is sent to the serverIDsigner
66- The serverIDsigner Blind Signs the Public-Key blinded from the user, and returns it to the user
67- The user unblinds the Public-Key signed by the serverIDsigner, and now has the Public-Key Blind Signed by the serverIDsigner
68- The user sends the Public-Key blind signed to the p2p network
69- The peers verify that the Public-Key Blind Signed is correctly signed by the serverIDsigner, if it is, they add the Public-Key to the Ethereum Blockchain, inside a new block
70
71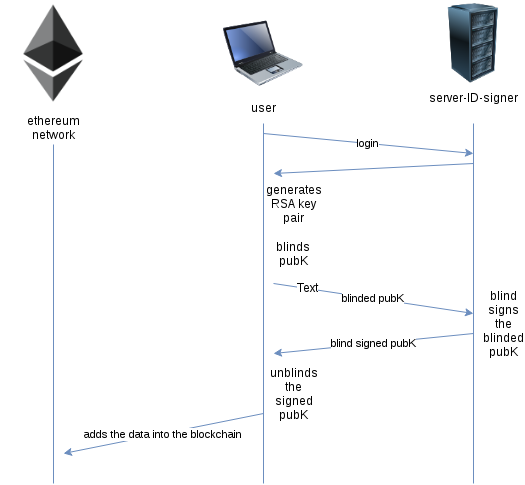
72
73- Then, when the user wants to login into a platform, just needs to put his Public-Key
74- The platform goes to the Ethereum Blockchain, to check if this Public-Key is registered in the blockchain
75- The platform sends a message encrypted with the user Public-Key, and the user returns the message decrypted with the Private-Key, to verify that is the owner of that Public-Key
76
77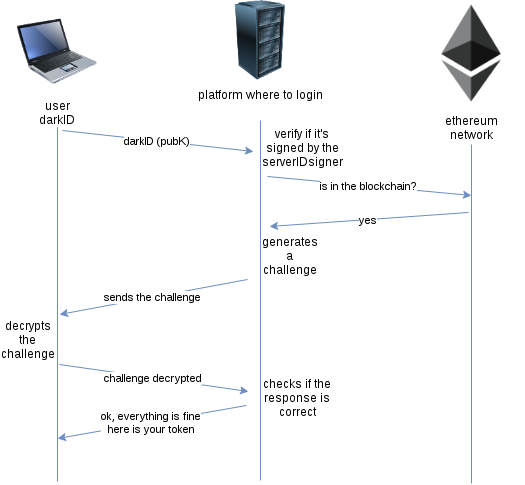
78
79The user Private Keys are stored only in the user local directory 'darkID/keys'.
80
81## 3.- Cryptography
82### 3.1.- RSA encryption system
83https://en.wikipedia.org/wiki/RSA_cryptosystem
84- Public parameters: (e, n)
85- Private parameters: (d, p, q, phi, sigma)
86- Public-Key = (e, n)
87- Private-Key = (d, n)
88- Encryption:
89
90- Decryption:
91
92
93
94### 3.2.- Blind signature process
95https://en.wikipedia.org/wiki/Blind_signature
96- m is the message (in our case, is the Public-Key of the user to be blinded)
97
98
99- serverIDsigner blind signs m'
100
101
102- user can unblind m, to get m signed
103
104
105- This works because RSA keys satisfy this equation
106 and this 
107
108
109## 4.- Conclusions
110- This is just a proof of concept, as an extra [project in a university small subject](https://github.com/arnaucode/darkID/blob/master/darkID-presentation.pdf). Is not a full finalized project.
111- Cryptographic [blind signature](https://en.wikipedia.org/wiki/Blind_signature) is very powerful, and also, can be combined with [homomorphic encryption](https://en.wikipedia.org/wiki/Homomorphic_encryption) properties, to make secure and anonymous systems.
112- In this proof of concept, the smart contract integration is not finished, and is using ethereum Smart Contracts, but can be implemented using any other blockchain technology. At the beginning [I tried to implement a complete p2p network and a blockchain from scratch](https://github.com/arnaucode/blockchainIDsystem) (but was not a good idea having a short amount of time).
113- A decentralized anonymized login system over blockchain, can have lots of applications for example, can be useful to authentication for centralized and decentralized platforms, for voting systems, for health systems, for exchanges, for anonymous reputation systems, etc.